


BOSTON, October 20, 2026. CyberSaint, delivering the Cyber Risk Intelligence Platform for large enterprises, has received Frost & Sullivan's 2026 Global Cyber Risk Management Competitive Strategy Leadership Recognition. Frost & Sullivan analysts spent 12 months evaluating cybersecurity risk and compliance vendors against ten criteria across strategy innovation and customer impact before selecting a winner for the award.
The report describes a market in transition. Enterprises are moving away from static, audit-driven assessments and siloed point solutions toward continuous cyber risk intelligence that ties millions of dynamic security data points to business impact. Frost & Sullivan found that CyberSaint “intentionally aligns its platform to the complexity, scale, and operational realities of large enterprises,” while many vendors target small and mid-sized businesses with simplified compliance tooling. As enterprises “replace fragmented, manual processes with centralized, intelligent systems,” the report concludes that demand is expected to accelerate, “positioning CyberSaint to capture a growing share of the market.”
AI is accelerating that shift. Enterprises can now automate far more of their security and risk work, but automation is only as good as the context behind it. An AI agent that doesn’t know which assets support which business processes, or what an exposure would cost, produces output nobody can defend. CyberStrong provides that context: the link between security data and business impact that makes AI output trustworthy enough to act on and defensible before a board or an auditor. Clients and partners are now building their own AI agents on top of the CyberStrong platform. The same need for context is moving enterprises off legacy GRC systems, which keep data in silos and can’t consume security telemetry at volume. It is also moving them off compliance automation tools built for smaller organizations, which lack the scale, defensibility, and breadth of integrated use cases an enterprise program requires.
“Collectively, these elements define CyberSaint’s competitive strategy: a combination of enterprise alignment, technological depth, AI-native innovation, and measurable value delivery,” said Vivien Pua, Industry Principal, Security, Frost & Sullivan. “The result is a platform that outperforms competitors on capability and performance and reshapes how organizations evaluate the true return on investment (ROI) in compliance and cyber risk management, shifting the conversation from cost centers to strategic enablers of resilience and business value.”
Why Frost & Sullivan Recognized CyberSaint
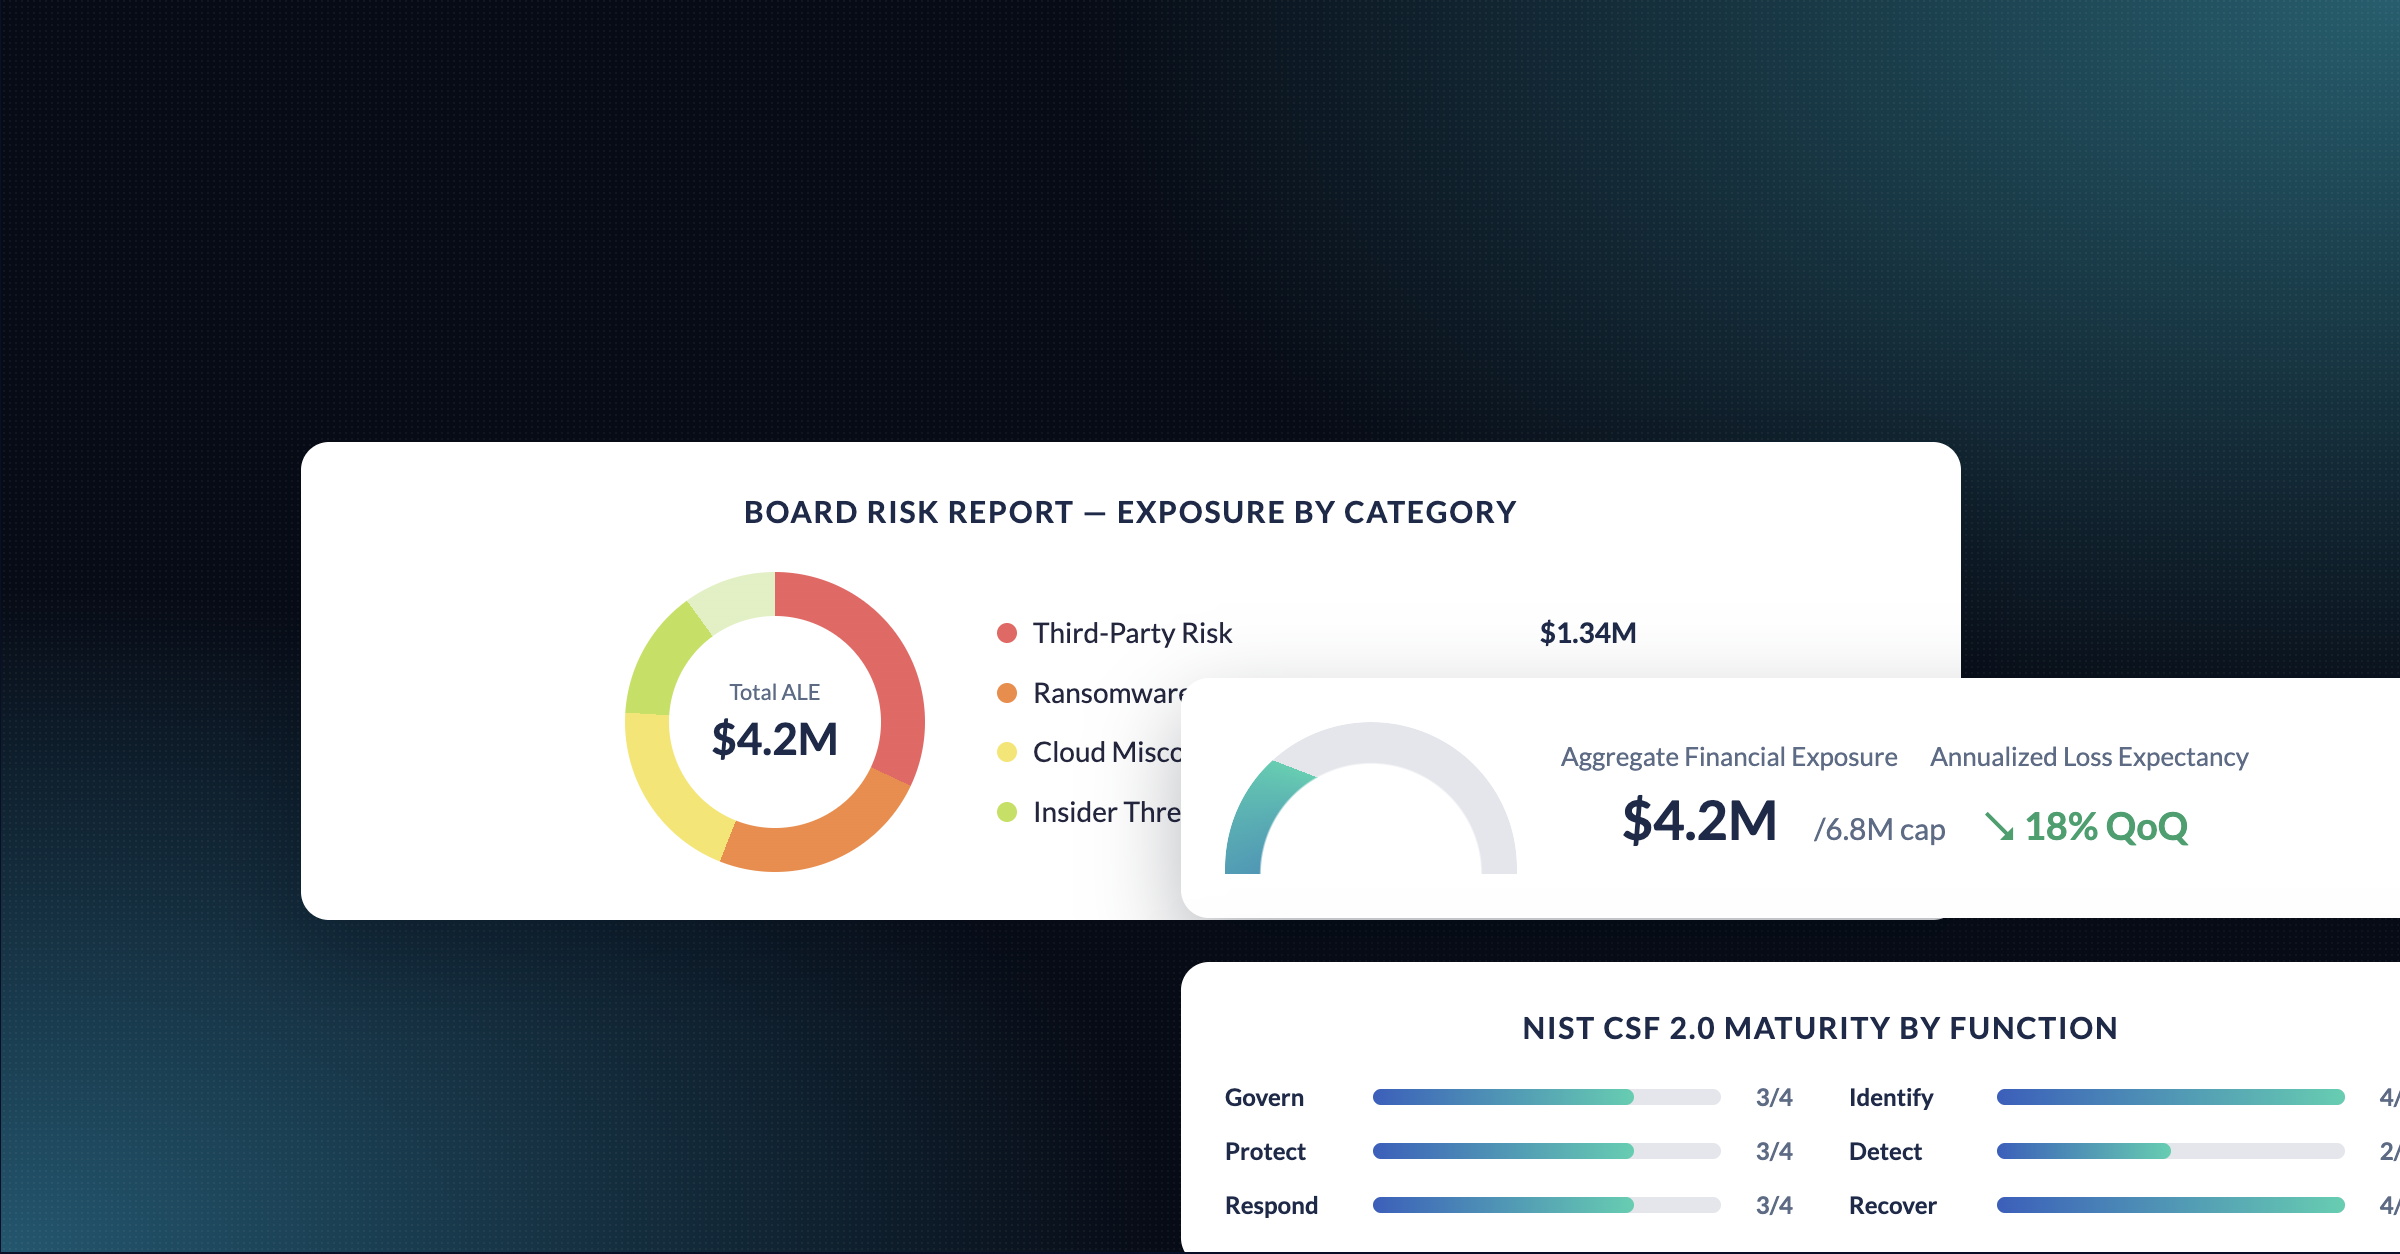
- Financially quantified cyber risk. CyberSaint’s cyber risk quantification links controls, vulnerabilities, threats, and business context into one model grounded in actuarial loss data and real-time system inputs. Enterprises see exposure in dollars and prioritize remediation by business impact, moving beyond qualitative scores and static heat maps.
- A transparent, defensible methodology. Customers can see how risk is calculated, how controls are mapped, and how every outcome is derived. Frost & Sullivan contrasted this with “competing solutions that rely on opaque scoring models,” and noted it is critical when reporting risk to executives and boards.
- AI-native architecture built for regulated industries. The CyberStrong solution combines large language models, graph neural networks, and task-specific models within constrained data environments. The report notes this produces consistent, audit-ready outputs, an area where many competitors still face skepticism. It calls the design a departure from “the bolt-on AI strategies commonly observed across the market.”
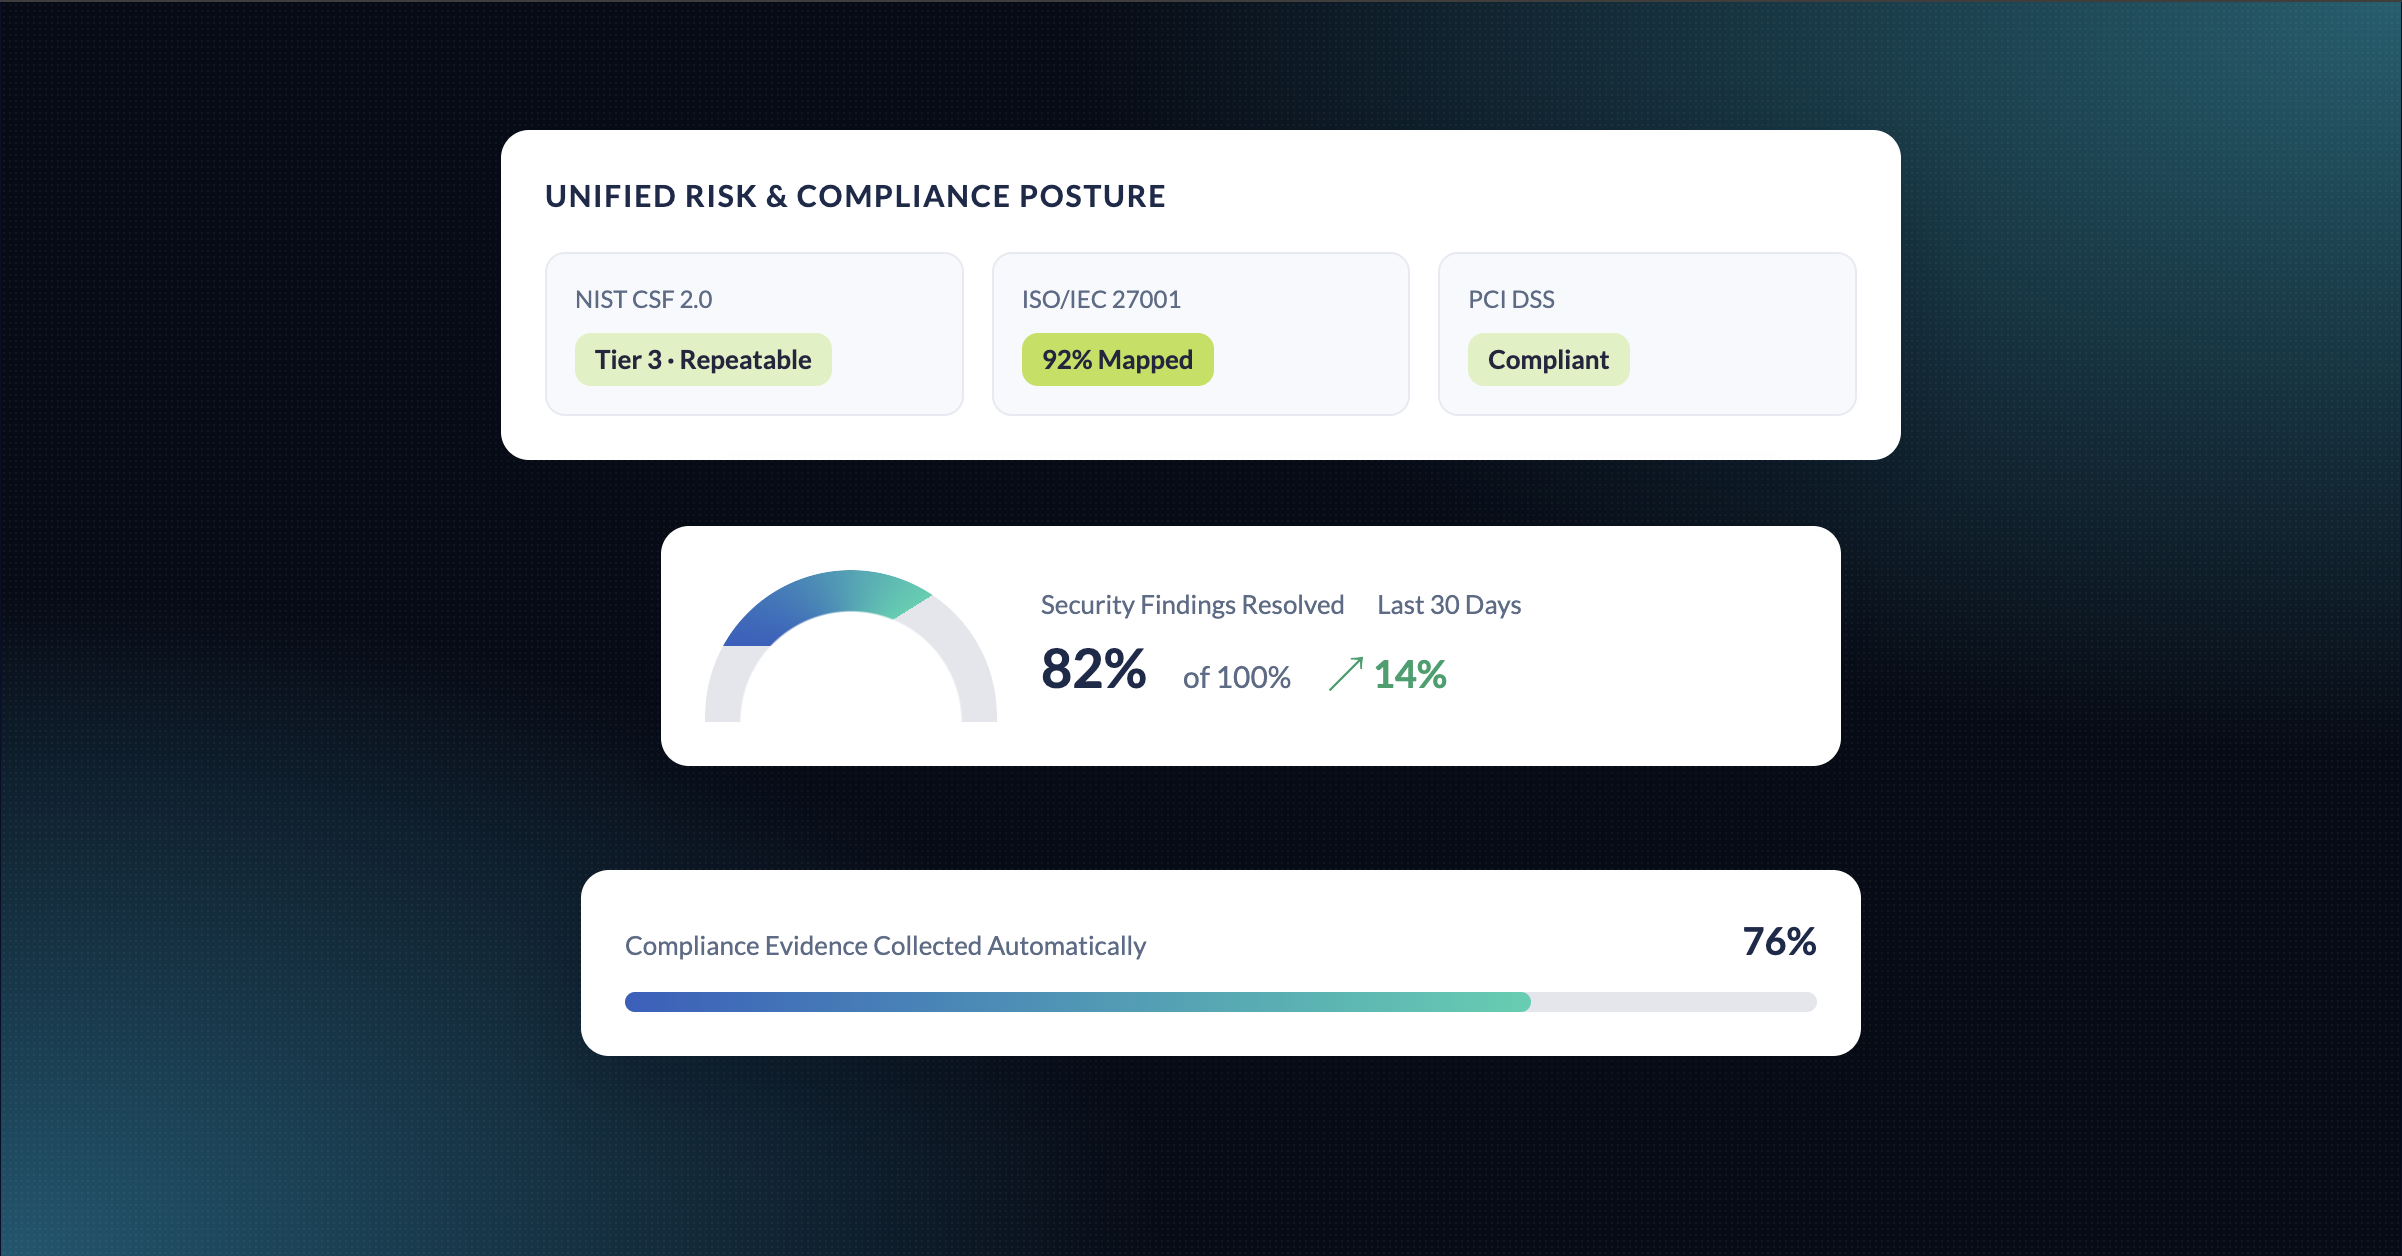
- One intelligence layer across a broad range of use cases. Frost & Sullivan wrote that CyberSaint “has defined a hybrid category” that integrates all security telemetry coming from inside and outside an enterprise into a unified, continuously updating system. Within a single platform, enterprises run cyber risk quantification and benchmarking, board reporting, risk-based prioritization, third-party risk management, continuous control monitoring, and policy management, with use cases frequently expanding.
- Output that scales without added headcount. Customers increase the scale and frequency of risk and third-party assessments and move to continuous monitoring without growing their teams. On average, CyberSaint customers increase third-party risk assessment volume by more than 100x and risk assessments on crown jewels by 400%, moving from a point-in-time to a continuous model and reducing cyber risk exposure by millions per year.
- Partner-led reach in regulated sectors. Frost & Sullivan cited CyberSaint’s strategic partnerships and its ecosystem of more than 100 channel and technology partners, which extend CyberSaint into regulated industries like insurance, financial services, technology, utilities, and transportation, and give the company a distribution advantage to the enterprise market.
“Frontier AI is changing the pace of this business, and boards want to know what that means for them in dollars,” said Jerry Layden, CyberSaint's CEO. “We decided early to build for the largest, most regulated enterprises, the ones that feel that pressure first. Frost & Sullivan spent over a year judging whether that choice held up in execution, and it did. Our customers pushed us to build what they actually needed. This recognition is as much theirs as ours, and I’m grateful to them, our partners, and a team that has not stopped delivering. The pressure isn’t going to let up, and neither are we. We’re going to keep executing, keep growing, and keep earning the trust they’ve given us.”
“AI can now reason across an enterprise’s entire security estate in seconds,” said Padraic O’Reilly, CyberSaint's Founder and Chief Innovation Officer. “Whether that reasoning can be trusted depends on the context underneath it. Cyber risk intelligence means knowing, in real time, which assets run which business processes, what a failure would cost, and exactly how we reached every number. We’ve spent years engineering that context and the logic that makes each answer defensible. It’s the foundation every security agent will run on, and it’s already built.”
The Frost & Sullivan recognition adds to a run of independent analyst validation for CyberSaint. In 2025, CyberSaint was named across four categories in the Gartner® Hype Cycle™ for Cyber Risk Management and in the Gartner® Hype Cycle™ for AI and Cybersecurity. CyberSaint was also recognized in the Gartner Market Guide for Third-Party Risk Management Technology Solutions, following its inclusion in the Cyber Risk Quantification Solutions Landscape, Q4 2024.
The full Frost & Sullivan report is available here. Enterprise security and risk leaders can schedule a demo of CyberSaint’s platform to see it in action.
About CyberSaint
CyberSaint is redefining how enterprises manage cyber risk through the CyberStrong cyber risk intelligence platform. The platform ingests millions of dynamic data points to give security leaders the context they need to quantify risk, monitor compliance, prioritize action, and prove ROI, automating what once took teams weeks or months. With AI and automation at its core, CyberSaint turns cyber risk management into a strategic advantage. Learn more at www.cybersaint.io.
About Frost & Sullivan
Frost & Sullivan’s Best Practices Recognitions honor companies across regional and global markets that exhibit exceptional achievement and consistent excellence in areas such as leadership, technological innovation, customer experience, and strategic product development. Each recognition is the result of a rigorous analytical process in which Frost & Sullivan industry experts benchmark performance through comprehensive interviews, deep-dive analysis, and extensive secondary research. The goal is to identify true best-in-class organizations that are driving transformative growth and setting new industry standards.
Contact us: Start the discussion.
Media contact
-
CyberSaint PR Team
-
media@cybersaint.io